
Are you using a VPN or proxy but still being detected, blocked, or having access restricted by websites? In some cases, the problem may not be your IP address but rather a DNS leak exposing your connection information.
In this guide, IPFighter explains what a DNS leak is, how it happens, the risks it creates, and how to prevent it.
1. What is a DNS leak?
Whenever you type a website address into your browser, your device sends a DNS request to translate that domain name into an IP address that computers can understand. This process normally happens in the background and takes only a fraction of a second.
A DNS leak occurs when these DNS requests are sent outside of the secure VPN or proxy connection and are instead routed directly to your internet service provider's DNS servers. As a result, third parties can still see which websites you are visiting even if your internet traffic is otherwise protected.
What is a DNS leak
Discover more:
-
What is DNS? How the DNS system works on the internet
-
What is an IP Address? Everything you need to know
-
What is WebRTC? Exploring its architecture, use cases, and benefits
2. How does a DNS leak happen?
Although VPNs and proxies are designed to protect internet traffic, DNS requests do not always follow the same secure path. Certain operating system settings, browser behaviors, or network configurations can cause DNS traffic to bypass the protected connection. A normal secure connection typically follows this path:
Your Device → VPN/Proxy Tunnel → VPN/Proxy DNS Server → Destination Website
In this scenario, both your browsing traffic and DNS requests are handled through the VPN or proxy provider's infrastructure. However, when a DNS leak occurs, the process looks different:
Your Device → ISP DNS Server or Your Device → VPN/Proxy Tunnel → Destination Website
In other words, the website traffic remains protected, but the DNS requests are sent directly to your ISP's DNS servers.
3. What information can a DNS leak expose?
At first glance, a DNS leak may seem less serious than an IP leak. However, DNS requests can reveal a surprising amount of information about your online behavior.
3.1. Browsing activity
The most obvious exposure is your browsing history. DNS requests contain the domain names you access, which means an observer may see websites such as: google.com, facebook.com, amazon.com, etc.
Even if the actual page content remains encrypted, the destination domains can still reveal significant information about your interests and activities.
3.2. Approximate location information
DNS servers often operate within specific regions or countries. When DNS requests are routed through local ISP infrastructure, observers may be able to infer your approximate geographic location.
This becomes particularly relevant when users attempt to appear in another country through a VPN while DNS requests continue using local DNS servers.
3.3. ISP visibility
Your ISP may be able to record DNS requests that pass through its infrastructure. As a result, the provider can potentially see which websites you visit, how frequently you visit them, and when those visits occur.
3.4. Corporate or public network monitoring
Organizations that manage public or corporate networks may also monitor DNS traffic. For example, schools, universities, offices, and public Wi-Fi providers may use DNS logs to monitor internet usage and enforce network policies.
Even if your browsing traffic is encrypted, DNS requests can still provide visibility into online activity. As a result, a DNS leak can create privacy risks even when your VPN or proxy appears to be functioning correctly.
Information that DNS leaks can reveal
4. What causes DNS leaks?
DNS leaks can occur for several different reasons. Understanding the most common causes can help users identify and prevent potential privacy issues.
-
VPN misconfigurations: If a VPN is not configured correctly, DNS requests may continue using the default DNS servers provided by the ISP instead of being routed through the VPN tunnel.
-
System or browser settings: Some operating systems and browsers may automatically select their preferred DNS servers or use features such as DNS-over-HTTPS (DoH), potentially bypassing the DNS settings configured by the VPN.
-
IPv6 DNS leaks: When a VPN only protects IPv4 traffic, DNS requests sent over IPv6 connections may bypass the secure tunnel and become exposed.
-
Smart DNS interference: Smart DNS services can sometimes override VPN DNS settings, causing DNS requests to be routed outside the VPN connection.
-
Transparent DNS proxies: Some ISPs automatically intercept and redirect DNS requests through their own DNS infrastructure, even when alternative DNS servers are manually configured.
Understanding these common causes can help you troubleshoot DNS leaks more effectively and maintain better online privacy.
5. How to check DNS leaks on IPFighter
A DNS leak can occur without any obvious warning signs, which is why regular testing is important. Fortunately, you can quickly verify whether your DNS requests are being routed correctly by using IPFighter's DNS leak testing tools.
When checking for DNS leaks, there are several key factors to review:
-
DNS provider identification: Verify which DNS servers are currently handling your DNS requests. If you're connected to a VPN/Proxy but still see your ISP's DNS servers, this may indicate a DNS leak.
-
DNS location analysis: Check whether the DNS server location makes sense relative to your VPN or proxy connection. The DNS location does not always need to exactly match the VPN location, as some providers operate DNS infrastructure in nearby countries or regions. For example, a VPN endpoint in Singapore may legitimately use DNS servers located in Hong Kong or Japan.
In addition to checking for DNS leaks, IPFighter can also help verify your IP reputation, analyze network information, and provide additional security diagnostics to ensure your connection is configured correctly.
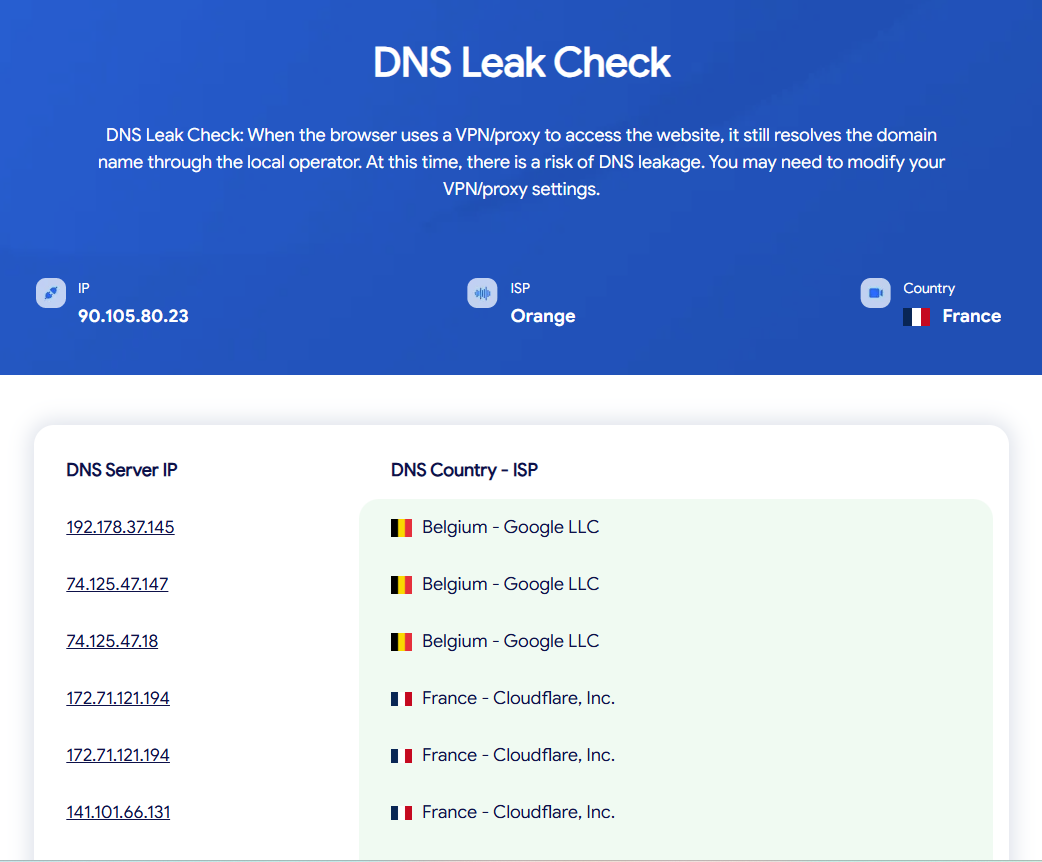
DNS leak check on IPFighter
In the example image above, the user's ISP is Orange (France), while the detected DNS servers belong to Google LLC (Belgium) and Cloudflare (France). Since the DNS requests are not being resolved by Orange's DNS servers, this result does not indicate a DNS leak. Instead, it suggests that DNS traffic is being routed through external DNS providers as intended.
Read more:
-
How to check IP reputation using IPFighter
6. How to fix and prevent DNS leaks
If a DNS leak is detected, there are several steps you can take to improve your privacy and prevent future leaks.
-
Force your VPN to use dedicated DNS servers: Configure your VPN to use its own DNS infrastructure or trusted DNS providers such as Cloudflare (1.1.1.1) to ensure DNS requests remain inside the protected tunnel.
-
Enable kill switch protection: Activate the VPN's kill switch feature to automatically block internet traffic if the VPN connection unexpectedly drops, preventing DNS requests from being routed through your ISP.
-
Configure secure DNS settings on your router: Set trusted DNS servers directly on your router to provide consistent DNS protection across all devices connected to your network.
-
Review browser DNS settings: Check whether features such as DNS-over-HTTPS (DoH) are overriding your VPN's DNS configuration and adjust settings if necessary.
-
Test regularly: Run DNS leak tests periodically, especially after changing VPN settings, updating software, or modifying your network configuration.
By following these best practices, you can significantly reduce the risk of DNS leaks and maintain better privacy while using VPNs and proxy services.
Fixing and preventing DNS leaks
7. Conclusion
A DNS leak occurs when DNS requests bypass your VPN or proxy connection and are sent directly to DNS servers outside the protected tunnel. Even when your browsing traffic is encrypted, this can expose information about the websites you visit and reduce your overall online privacy.
Regular DNS leak testing is one of the simplest ways to verify that your VPN or proxy is working properly. Use IPFighter to detect DNS leaks, analyze DNS servers, and evaluate whether your connection is providing the level of privacy you expect.
8. FAQ
What is a DNS leak?
A DNS leak occurs when your computer mistakenly routes its domain lookup queries directly to your local internet provider's DNS servers outside your active VPN or proxy tunnel, exposing your web history despite your changed IP address.
Is a DNS leak dangerous?
A DNS leak does not always expose your real IP address, but it can reveal the websites you visit and reduce your online privacy.
Does a DNS leak expose my IP address?
Not necessarily. A DNS leak primarily exposes DNS requests, while your actual IP address may remain hidden. To understand the difference, it helps to learn what an IP address is and how IP-based identification works.
How do I test for a DNS leak?
You can use DNS leak testing tools such as IPFighter to identify which DNS servers are processing your DNS requests and determine whether traffic is being routed correctly.
What causes DNS leaks?
Common causes include VPN misconfigurations, browser settings, IPv6 traffic, Smart DNS conflicts, and transparent DNS proxies operated by ISPs.
Can proxies prevent DNS leaks?
Some proxies can help route DNS requests correctly, but not all proxy configurations provide DNS leak protection. Testing is recommended to verify proper operation.
What is the difference between a DNS leak and an IP leak?
A DNS leak exposes the domains you visit through DNS requests, while an IP leak reveals your actual IP address. Both can negatively affect online privacy.
Read more
VPN checker: 4 signs your VPN is detected and how to check
What is a clean IP address and how does it work?
What is Scamalytics? 4 Fraud Score risk levels
DNS blacklist: How to check and remove your IP
Why Google says "Unusual traffic from your computer network"
Anonymous proxy detected: Causes and how to fix it