
Why does one network load websites almost instantly while another takes noticeably longer, even though both use the same internet connection? One reason is how DNS requests are handled behind the scenes. Many businesses and organizations improve both speed and security by using DNS forwarding.
In this guide, IPFighter explains what DNS forwarding is, how it works, why organizations use it, and how it helps optimize DNS performance while reducing security risks.
1. What is DNS forwarding?
DNS forwarding is the process of sending unresolved DNS queries from one DNS server to another designated DNS server, known as a DNS forwarder, instead of performing the entire recursive lookup (a process where a DNS server queries multiple DNS servers across the internet until it finds the correct answer) itself.
To understand this process, it first helps to know “what is DNS” and how domain name resolution works.
Normally, a DNS server attempts to resolve a domain by checking its own records, cache, or performing recursive queries across the DNS hierarchy. With DNS forwarding enabled, however, the local DNS server delegates that responsibility to another trusted DNS server whenever it cannot answer a request locally.
For example: Think of a DNS forwarder like the receptionist in a large office building. If someone asks a question the receptionist already knows, they answer immediately. If not, instead of searching every department themselves, they simply forward the request to the right person who already has the answer. DNS forwarding works in much the same way.
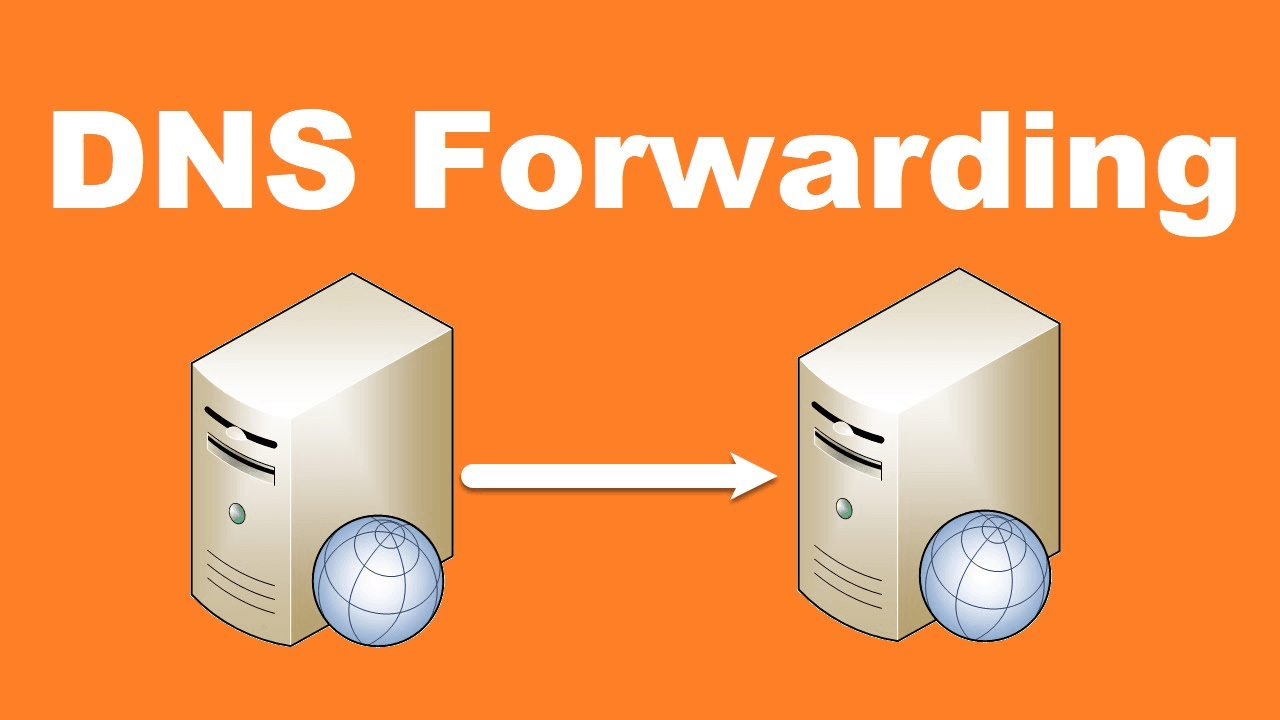
Definition of DNS forwarding
Discover more:
-
DNS records - The ultimate blueprint for website & email routing
-
How to flush DNS on Windows, Mac, and Linux in simple steps
2. How does DNS forwarding work?
DNS forwarding only comes into play when a DNS server cannot answer a query using its own information. Instead of performing a full recursive lookup across the internet, it simply forwards the request to another DNS server that has already been configured as the forwarder. Imagine you type google.com into your browser. Here's what typically happens:
-
Step 1: Your computer sends a DNS request to your local DNS server asking, "Where is google.com?"
-
Step 2: The local DNS server first checks whether it already knows the answer. It looks in: its own DNS records, its cache (previous DNS answers that are still valid)
-
Step 3: If it still doesn't know the answer, instead of searching the internet itself through a process called a recursive lookup (asking multiple DNS servers until the correct answer is found), it forwards the request to a trusted DNS forwarder.
-
Step 4: The DNS forwarder resolves the domain name and sends the result back.
-
Step 5: Your browser receives the IP address and connects to the website.
In many cases, the DNS server will temporarily store the result in its cache (based on the record's TTL), allowing future requests for the same domain to be answered much faster.
How is this different from an iterative query? In an iterative query, a DNS server replies with the best answer it has, often a referral to another server, and the asking server follows the chain from the root servers to the top-level domain servers and then to the authoritative server. A recursive query asks the server to return the final answer or an error.
When a DNS server uses a forwarder, it sends a recursive query to the forwarder. Without a forwarder, it resolves names itself with iterative queries starting from its root hints, which can expose internal DNS information to the internet and create more external traffic.
3. Why use DNS forwarding?
DNS forwarding offers several advantages beyond simply passing DNS queries to another server. It can improve network performance, simplify DNS administration, and strengthen overall security. Here are some of its biggest benefits:
-
Faster DNS resolution: Forwarders often maintain large DNS caches, allowing them to answer frequently requested queries without performing a full DNS lookup. This reduces latency and helps users access websites more quickly.
-
Reduced DNS traffic: Instead of every DNS server performing its own recursive lookups, multiple servers can rely on a shared forwarder. This minimizes duplicate queries, reduces bandwidth usage, and lowers the workload on DNS infrastructure.
-
Centralized DNS management: Organizations can configure a single DNS forwarder to handle external DNS resolution for the entire network. This makes it easier to manage DNS policies, logging, and security settings from one location.
-
Better security: Forwarding queries to trusted DNS providers that offer threat protection can help block requests to malicious domains, phishing websites, and malware-hosting servers before users connect to them.
-
Improved access control: Administrators can control where different DNS queries are sent. For example, internal company domains can be resolved by private DNS servers, while public internet domains are forwarded to external resolvers, improving both security and operational efficiency.
Overall, DNS forwarding helps organizations optimize DNS resolution by improving performance, reducing administrative overhead, and creating a more secure and manageable DNS infrastructure.
The benefits of DNS forwarding
4. Types of DNS forwarding
Not all DNS forwarding works in the same way. Depending on how queries are routed, DNS forwarding generally falls into two main categories: global forwarding and conditional forwarding. Understanding the difference between these two methods helps administrators choose the right configuration for their network.
4.1. Global forwarding
Global forwarding sends all unresolved DNS queries to one or more designated upstream DNS servers (another DNS server responsible for resolving queries on behalf of your local server). When the local DNS server cannot answer a request using its own records or cache, it automatically forwards the query to the configured forwarder instead of performing recursive lookups itself.
This approach is commonly used in organizations that want to centralize external DNS resolution while reducing the workload on local DNS servers. Some of the main advantages of global forwarding include:
-
Simple to configure: Only one set of forwarders needs to be configured for all external DNS requests.
-
Improved performance: Frequently requested domains can be resolved quickly thanks to the forwarder's larger DNS cache.
-
Easy redundancy: Multiple forwarders can be configured so that if the primary DNS forwarder becomes unavailable, queries are automatically sent to a backup server.
Global forwarding is often the best choice for businesses that want a simple, centralized DNS architecture without creating separate routing rules for different domains.
4.2. Conditional forwarding
Conditional forwarding is more selective. Instead of forwarding every unresolved DNS query, the DNS server only forwards queries for specific domain names to designated DNS servers.
For example: Queries for company.local may be forwarded to an internal corporate DNS server. Queries for partner.example.com may be forwarded to a partner organization's DNS infrastructure. All other internet domains can continue using public DNS resolvers.
Some benefits of conditional forwarding include:
-
More precise routing: Different domains can use different DNS servers.
-
Improved performance for internal services: Internal resources can be resolved directly without unnecessary recursive lookups.
-
Better security: Sensitive internal DNS traffic remains inside the organization's network whenever possible.
Conditional forwarding is particularly useful when organizations need to connect multiple private networks while keeping DNS resolution efficient and well organized.
5. How to set up DNS forwarding
The exact steps depend on the DNS software you run. Below are example configurations for three common setups. Replace the IP addresses with your own DNS servers and check the official documentation for your version.
5.1. Windows Server
On Windows Server, forwarders are set at server level, and conditional forwarders are created as forwarder zones. You can manage both with PowerShell:
Set-DnsServerForwarder -IPAddress 1.1.1.1, 9.9.9.9
Add-DnsServerConditionalForwarderZone -Name "partner.example.com" -MasterServers 10.0.0.5
The server tries forwarders in the order they are listed, and by default it reorders them dynamically by response time. From Windows Server 2022, if no forwarder responds, the server keeps using only the first one on its dynamic list until the DNS service restarts. Check the exact syntax in Microsoft's documentation for the cmdlets.
5.2. BIND
In BIND, forwarders are set in the options block, and conditional forwarding uses a zone of type forward:
options {
forwarders { 1.1.1.1; 9.9.9.9; };
forward first;
};
zone "partner.example.com" {
type forward;
forwarders { 10.0.0.5; };
forward only;
};
With forward first, the server tries the forwarders first and then falls back to resolving the name itself if they do not answer. With forward only, it never falls back.
5.3. pfSense
In pfSense, go to Services, then DNS Resolver, and turn on Enable Forwarding Mode. The resolver then forwards queries to the DNS servers listed under System, General Setup, and you can send those forwarded queries over DNS over TLS for more privacy. To send specific domains to specific DNS servers, use Domain Overrides.
These are examples only, and menus and syntax can change between versions. For the official steps, see Microsoft Learn on DNS forwarding in Windows Server, the Netgate guide to DNS Resolver modes, and the BIND 9 Administrator Reference Manual.
6. How DNS forwarding impacts security
While forwarding provides clear speed advantages, changing how your network handles naming requests introduces important security considerations that require careful management.
-
Proactive threat protection: Security-focused DNS forwarders such as Quad9 or OpenDNS can automatically block requests to malicious domains, phishing websites, and malware-hosting servers before users establish a connection.
-
Potential DNS leak risks: If DNS forwarding is configured incorrectly, DNS requests may bypass the intended forwarder and be sent through your ISP's DNS servers instead. This can expose your real network information and reduce the privacy benefits of VPNs or proxies.
For example, imagine you're connected to a VPN that should route all of your traffic through its own secure DNS servers. If your DNS requests are accidentally sent to your ISP's DNS servers instead, websites and online services may still learn information about your network or approximate location, even though your IP address appears to come from the VPN.
To get the most out of DNS forwarding, it's important to verify that your DNS queries are being routed correctly and that no DNS leaks are exposing your network information.
7. Check and verify your DNS with IPFighter
After configuring DNS forwarding, it's important to verify that your DNS requests are being routed as expected. IPFighter provides information to help you check your current DNS configuration and identify potential problems before they affect your privacy or network performance:
-
Check for DNS leaks: Verify whether your DNS requests are being sent through the intended DNS server or accidentally leaking to another resolver.
-
Review DNS server information: See which DNS servers are currently resolving your queries.
-
Validate proxy and VPN configurations: Confirm that your DNS traffic follows the same route as your proxy or VPN connection.
Regularly testing your DNS setup helps ensure that your forwarding configuration works as intended and that your network remains both efficient and secure.
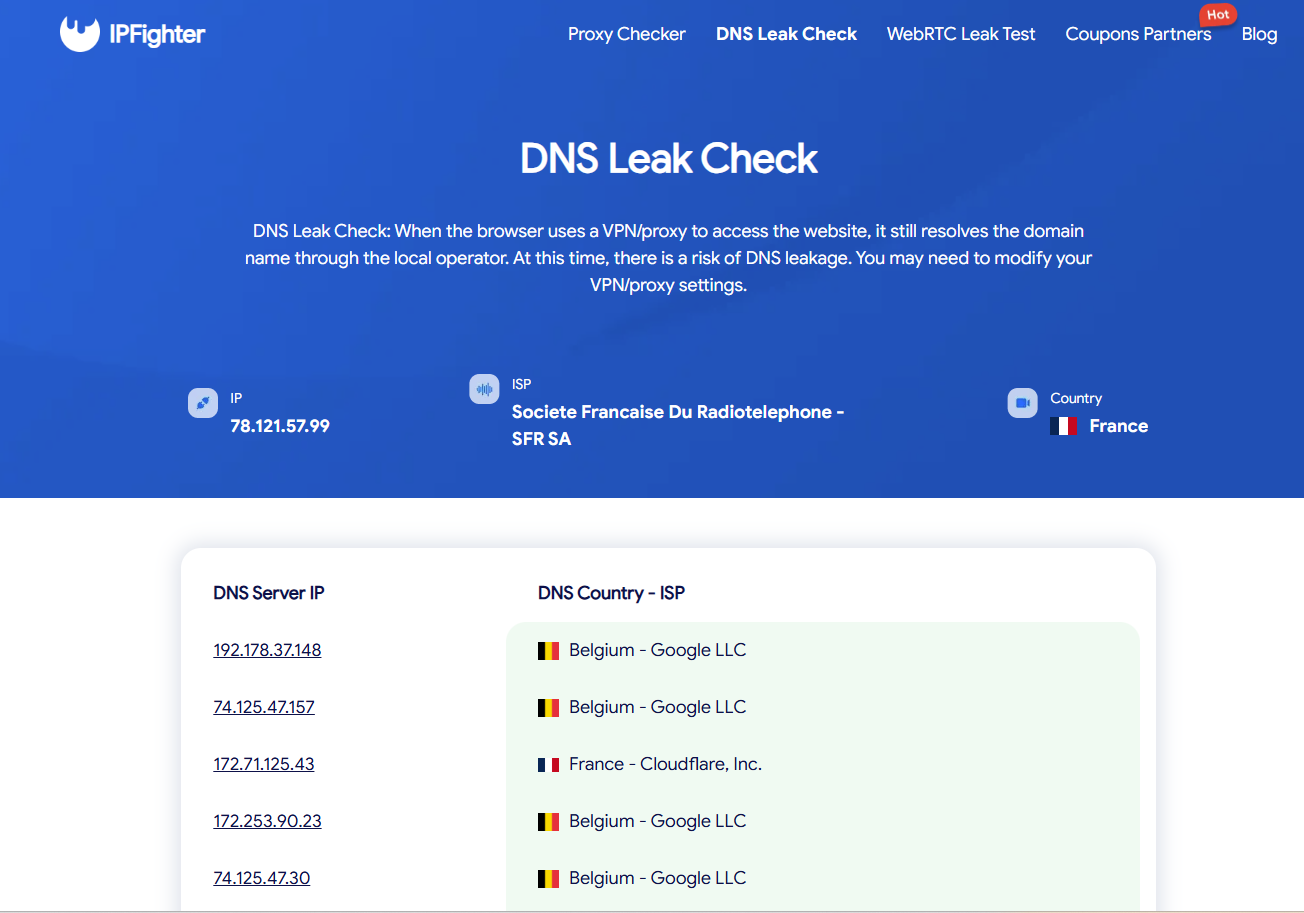
Check DNS leak on IPFighter
Read more:
-
How to check IP reputation using IPFighter
-
What is an IP Address? Everything you need to know
8. Best practices for DNS forwarding
DNS forwarding is relatively simple to configure, but following a few best practices can improve both performance and security over the long term.
-
Choose a trusted upstream DNS provider: Use reputable DNS resolvers such as Cloudflare, Google Public DNS, Quad9, or OpenDNS to ensure fast, reliable, and secure DNS resolution.
-
Enable DNS caching: Caching allows frequently requested domains to be resolved more quickly, reducing latency and minimizing unnecessary DNS traffic.
-
Configure backup forwarders: Always specify multiple upstream DNS servers so queries can still be resolved if the primary forwarder becomes unavailable.
-
Put your most reliable forwarder first: Some DNS servers, such as Windows Server, try forwarders in the order they are listed, so the first entry should be the most dependable one.
-
Use encrypted DNS to upstream servers: Where your software supports it, send forwarded queries over DNS over TLS or DNS over HTTPS so they cannot be read on the way to the forwarder.
-
Monitor DNS logs: Regularly review DNS query logs to identify unusual traffic patterns, configuration issues, or potential security threats.
-
Keep DNS software up to date: Installing the latest updates helps protect your DNS infrastructure against newly discovered vulnerabilities and improves overall stability.
-
Combine forwarding with DNS security features: If available, choose forwarders that offer malware filtering, phishing protection, or threat intelligence to strengthen your network's defenses.
Finally, don't forget to periodically clear your DNS cache when making DNS changes or troubleshooting resolution issues. If you're unsure how to do this, our guide on how to flush DNS walks through the process on Windows, macOS, and Linux.
9. Conclusion
DNS forwarding is a simple yet powerful technique that improves how DNS queries are resolved across a network. By forwarding requests to trusted upstream DNS servers, organizations and individuals can reduce DNS traffic, speed up domain resolution, simplify DNS management, and enhance security.
However, proper configuration is essential. Choosing reliable DNS forwarders, monitoring for DNS leaks, and regularly verifying your DNS setup will help ensure your network remains both efficient and secure.
10. FAQ
What is DNS forwarding?
DNS forwarding is the process of sending unresolved DNS queries from one DNS server to another designated DNS server, known as a DNS forwarder, instead of performing recursive lookups itself.
What is the difference between DNS forwarding and recursive DNS?
A recursive DNS server resolves queries by contacting multiple DNS servers directly, while a DNS forwarder simply passes unresolved requests to another DNS server for resolution.
What is an iterative DNS query?
An iterative DNS query is a request where the server replies with the best answer it has, often a referral to another DNS server, and the requester follows the chain from the root servers to the authoritative server itself. By contrast, a DNS server that uses a forwarder sends it a recursive query and gets the final answer back.
What is conditional DNS forwarding?
Conditional DNS forwarding routes DNS queries for specific domain names to designated DNS servers, while all other queries continue to use the default forwarder.
Does DNS forwarding improve performance?
Yes. DNS forwarders often maintain large caches, allowing frequently requested domains to be resolved faster and reducing overall DNS lookup time.
Is DNS forwarding secure?
It can be. Using trusted DNS forwarders with malware and phishing protection can improve security, but incorrect configurations may lead to DNS leaks.
Should I use Google DNS or Cloudflare DNS as a forwarder?
Both are reliable choices. Cloudflare is known for its focus on privacy and speed, while Google Public DNS offers excellent reliability and global availability. Quad9 (9.9.9.9) is another option if you want built-in blocking of malicious domains.
Can DNS forwarding reduce DNS lookup time?
Yes. By forwarding requests to DNS servers with larger caches and optimized infrastructure, DNS forwarding can significantly reduce lookup latency for frequently accessed domains.
Read more
VPN checker: 4 signs your VPN is detected and how to check
What is a clean IP address and how does it work?
What is Scamalytics? 4 Fraud Score risk levels
DNS blacklist: How to check and remove your IP
Why Google says "Unusual traffic from your computer network"
Anonymous proxy detected: Causes and how to fix it