
A flagged abuse IP can silently derail your automation or account management before you even get started. Since modern security filters treat connection history as a primary trust signal, a tainted IP reputation is a massive bottleneck.
In this guide, IPFighter breaks down how IP abuse occurs and how you can protect your digital presence from inheriting a bad reputation.
1. What is an abuse IP?
At its core, an abuse IP refers to an IP address that has been detected and reported for suspicious or malicious behavior. This can range from sending unsolicited spam emails to launching full-scale cyberattacks.
To understand this, we first need to look at what is an ip address. It is a unique identifier for a device on a network. When an address is flagged for abuse, it means that global security databases and anti-fraud systems have associated that specific identifier with high-risk activities such as fraud, botnets, or phishing.
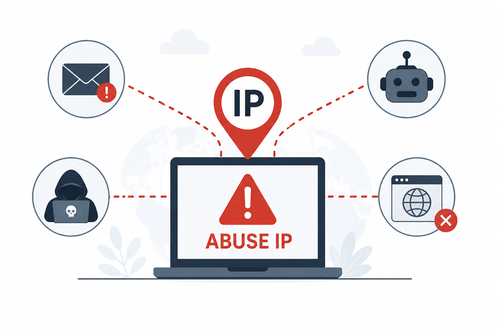
What is an abuse IP?
The consequences of using abused IP addresses are severe, impacting email deliverability, website accessibility, cybersecurity risks, user trust, and brand reputation.
One important thing to note is that an abuse IP is not always permanently malicious. In many cases, the IP itself is technically normal, but its historical behavior has damaged its reputation in security databases. This happens frequently with recycled IPs, shared proxies, VPN servers, and dynamic residential connections where multiple users may have previously used the same address for suspicious activities.
2. What triggers an IP abuse flag?
An IP address doesn't wake up one day and decide to be bad. It becomes an abuse IP through a series of logged events tracked by anti-fraud systems and blacklist databases (like Spamhaus or AbuseIPDB). These systems act as a global neighborhood watch, monitoring IP reputation in real-time.
An IP typically receives an abuse flag when it triggers specific red flags:
-
Spikes in traffic: A sudden burst of thousands of requests to a single server in seconds is a classic sign of a DDoS attack or a bot.
-
Repetitive bot behavior: Performing the same action (like clicking a button or refreshing a page) at exact intervals suggests automation rather than human browsing.
-
Security check failures: Constantly failing CAPTCHAs or triggering Web Application Firewalls will quickly degrade an IP's standing.
-
Linked account bans: If multiple accounts on a platform (like Facebook or Amazon) are banned while using the same IP, the IP itself is often burned and flagged for abuse.
-
IPs abused by previous users: In some cases, even if a user doesn't spam directly, they may still suffer from the bad history of an IP that was previously abused. This is an example of this happening when using shared proxies.
Repetitive behavior in bots is one of the warning signs
A crucial point to note is that modern anti-fraud systems rarely judge an IP based on a single action. Instead, they rely on behavioral pattern analysis over time. For instance, sending 100 requests isn't inherently abusive; however, executing those 100 requests within a few seconds, following an identical and predictable path across multiple pages, will immediately trigger a high-risk alert.
3. Common types of IP abuse
IP abuse can happen in many different forms. Some abuse types are relatively harmless, while others are considered serious cybersecurity threats. Understanding these categories helps explain why certain IPs become heavily restricted across platforms.
3.1. Spam abuse
This is the most common form. It includes:
-
Email spam
-
Comment spam
-
Fake traffic generation
Regardless of the specific method, these spamming activities are the primary drivers behind plummeting trust scores and immediate blacklisting by global mail and web servers.
Spam abuse is one of the fastest ways for an IP to become globally blacklisted because email providers and anti-spam organizations continuously exchange reputation data with each other. Once an IP is listed in major spam databases, even legitimate traffic from that address may start experiencing delivery failures or trust issues.
3.2. Bot & automation abuse
Websites hate unauthorized automation because it drains their resources. Abuse flags are raised for:
-
Excessive scraping
-
Mass account creation
-
Credential stuffing
-
Automated login attempts
Platforms often monitor how requests behave rather than simply counting them. If traffic patterns look too robotic, the IP may receive lower trust ratings. This is particularly important for users running scraping tools or automation software at scale.
3.3. Fraud & malicious activity
This is the darkest side of IP abuse, often involving criminal intent:
-
Hosting phishing pages
-
Malware distribution
-
Suspicious payment activity
-
Scam traffic
These activities usually lead to severe blacklist penalties because they directly threaten user security. Once an IP becomes associated with cybercrime databases, recovering its reputation can become very difficult.
3.4. Shared proxy and VPN abuse
Shared resources are the most common cause of IP reputation decline. When using cheap or free shared proxies and VPNs, you're sharing that IP address with hundreds of other people. If just one of those users decides to send spam, the entire IP address will be flagged. This is why public proxies almost always have a very poor IP reputation.
The severity of abuse consequences depends heavily on the platform being targeted. Social media platforms, payment gateways, advertising systems, and ecommerce marketplaces usually enforce much stricter IP reputation requirements than regular websites.
For example, an IP that works perfectly fine for browsing news sites may still fail when attempting account registration, ad management, or payment verification tasks.
Spam abuse is one of the most common types of IP abuse
4. How to check if an IP has abuse history
Not all risky IPs are obviously blocked. Some may still work normally while quietly carrying negative trust signals in the background. This is why checking an IP before using it for important tasks is highly recommended.
With IPFighter, users can quickly analyze multiple trust signals to evaluate IP quality. When auditing an IP, you should look for several key signals:
-
Platform trust score: Does the IP have a high ip trust score across major platforms like Google, Facebook, or Amazon?
-
Proxy/VPN detection: Is the IP recognized as a high-risk public proxy or a VPN rather than a clean residential or ISP IP?
-
Leak tests: Ensure your real identity is not leaked through WebRTC leak test or DNS leak check.
By verifying these metrics, you ensure that you aren't starting your project with a handicap caused by someone else's past mistakes. For professional users, regularly auditing proxy quality has become a standard operational practice. Monitoring reputation signals early allows teams to replace problematic IPs before they begin affecting performance or triggering account restrictions.
Many users only realize their IP has abuse history after encountering repeated CAPTCHAs, login verification loops, or sudden account restrictions. Unfortunately, by the time these symptoms appear, the IP reputation may already be severely damaged. Performing an IP audit before using an address for important activities can save both time and operational costs.
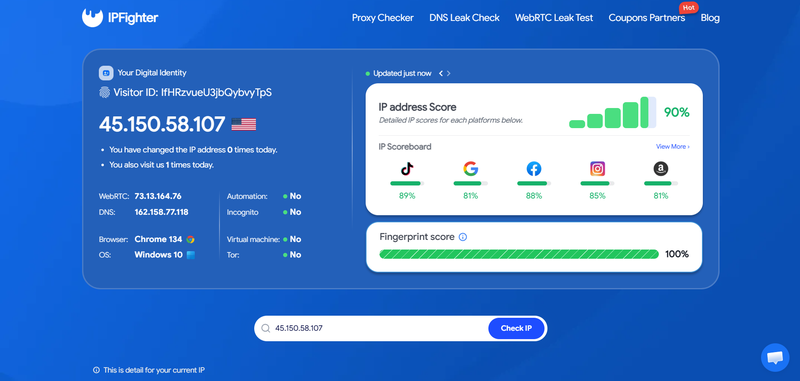
IP check on IPFighter
Read more:
-
What is WebRTC? Exploring its architecture, use cases, and benefits
-
What is DNS? How the DNS system works on the internet
5. Conclusion
An abuse IP is a major roadblock in the digital world. Whether it's the result of direct malicious intent or simply the bad luck of inheriting a recycled address with a dark history, a flagged IP will lead to CAPTCHAs, blocks, and account restrictions.
Understanding the mechanics of IP abuse is the first step toward maintaining a clean digital presence. Always prioritize quality over quantity. If you are looking for high-quality, non-abused addresses, we recommend sticking to reputable providers. To help you get started, you can explore our curated list of proxy promo codes and exclusive offers from our partner providers. This allows you to secure clean, high-reputation IP pools at a fraction of the cost, ensuring your automation remains smooth and undetected.
6. FAQ
What is an abuse IP?
An Abuse IP is an address that has been reported to security databases for participating in malicious activities like spam, bot attacks, or fraud.
Can a clean IP become an abuse IP?
Yes. If the IP is used to send spam, perform excessive scraping, or trigger security firewalls repeatedly, its ip trust score will drop, and it will eventually be flagged for abuse.
Does abuse IP always mean the IP is dangerous?
Not necessarily for the user, but it is "dangerous" for your project success. An Abuse IP might not steal your data, but it will get you blocked from the websites you are trying to access.
How do websites detect IP abuse?
Websites use anti-fraud services that check the ip reputation against global databases. They also monitor real-time behavior like request frequency and failed login attempts.
Can shared proxies become abuse IPs?
Very easily. Because multiple people use the same IP, the bad behavior of one user can cause the IP to be flagged for everyone else sharing it.
How can I check whether an IP has abuse history?
The most reliable way is to use an IP auditing tool like IPFighter. It provides a comprehensive breakdown of the IP's history, blacklist status, and overall trust level.
Read more
VPN checker: 4 signs your VPN is detected and how to check
What is a clean IP address and how does it work?
What is Scamalytics? 4 Fraud Score risk levels
DNS blacklist: How to check and remove your IP
Why Google says "Unusual traffic from your computer network"
Anonymous proxy detected: Causes and how to fix it